AppTrana WAAP’s adaptive rate-limiting capabilities suggest price limits by evaluating consumer behavior throughout URI, IP, session/host, and geography. This enables custom-made limits for endpoints like ‘/login’ versus ‘/dashboard’ and adjusts based on IP and geography. While seeing high demand on your API is encouraging, permitting unrestricted access can result in misuse and potential security vulnerabilities, such as DoS assaults. API Gateways offer features similar to API key management, OAuth/OIDC (OpenID Connect) support, fee limiting, caching, and logging.
A dedicated API safety https://logotype.dev/articles/how-to-create-a-watermark-logo-that-adds-a-professional-touch-to-your-branding platform is a specialised resolution to protect APIs from numerous threats and vulnerabilities. These platforms/appliances sometimes supply complete security features and capabilities tailored specifically for API protection. WAAP solutions provide complete protection for applications and APIs by inspecting incoming visitors, filtering out malicious requests, and implementing security insurance policies to stop assaults.
Key Options To Search For In Api Security Instruments
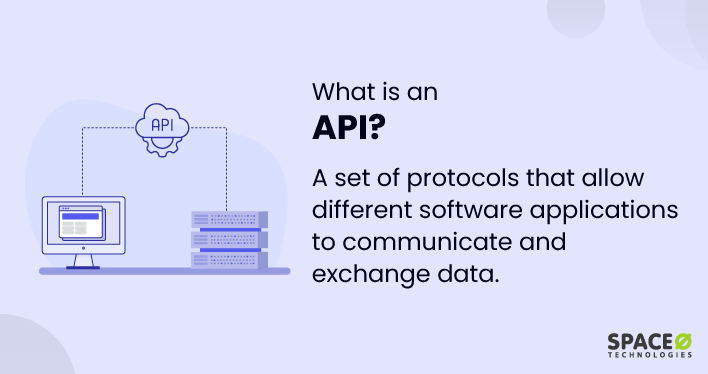
An API endpoint is the point at which an API communicates with another system—in other words, the URLs or digital areas the API makes use of to send information. API endpoints are necessary as a result of they provide the exact location of the info or sources the API is accessing and make sure that the system speaking with the API is functioning optimally. Encryption works by disguising data http://bgfashionzone.com/technology-and-freedom.html at one end of the communication and solely permitting it to be deciphered at the different finish if the correct decryption key is used. Otherwise, the encrypted data is a nonsensical jumble of characters, numbers, and letters. Encryption supports API security by making information unreadable to unauthorized users whose units cannot decipher the info. Easy Object Access Protocol (SOAP) is a messaging protocol based mostly on Extensible Markup Language (XML).

The Best Open-source Api Security Instruments And When To Use Them
This integration offers unified entry to its software security products like WAF, DDoS Protection, and Superior Bot Protection (ABP). By analyzing historical data saved in a devoted data lake, organizations acquire useful insights into past API interactions. Cloudflare’s answer is suitable for those looking for an alternative alternative to existing gateways that are expensive, influence performance, and pose information and privateness risks.
A Information To Integrating Utility Safety Tools Into Ci/cd Pipelines
It is essential to protect data, particularly given the rise of data-dependent tasks. On the API degree, security works by analyzing the information shifting into the API setting. On the appliance degree, API security blocks attempts to make the applying malfunction or to permit other customers to get inside and steal sensitive information. REST API helps safe sockets layer (SSL), transport layer safety (TLS), and Hypertext Switch Protocol Safe (HTTPS) protocols, which provide security by encrypting information during the transfer process. You can also safe REST APIs with tokens used to make sure communications are legitimate before allowing them to go through. The API safety firms should also maintain their security certifications, demonstrating their dedication to security best practices.
- AppTrana leads the way in which with its innovative approach to risk-based, totally managed API safety options.
- It additionally includes measures for bot protection, DDoS prevention, and access management, making certain complete defense.
- Machine learning-enabled real-time monitoring is especially effective at detecting anomalies in API visitors.
- Imperva API Security ensures complete API discovery and classification of sensitive information.
- The positive security mannequin works by allowing only what’s approved and blocking anything else.
- Fine-grained entry controls permit you to set particular permissions for users or systems, enforcing least-privilege entry to sensitive capabilities.
When the person uses Google Maps, they aren’t using code the online designer wrote piece by piece, but they are merely using a prewritten API offered by Google. Cequence and Salt Security achieved best-in-class within the 2023 Datos Insights Vendor Information. Cequence (96.3%) edged out Salt Security (92.4%), mainly within the vendor stability class. Broken API authentication is an API safety danger that happens when an API doesn’t properly examine and confirm who’s making a sure request.